





A poisoned launch of LiteLLM turned a routine Python set up right into a crypto-aware secret stealer that looked for wallets, Solana validator materials, and cloud credentials each time Python began.
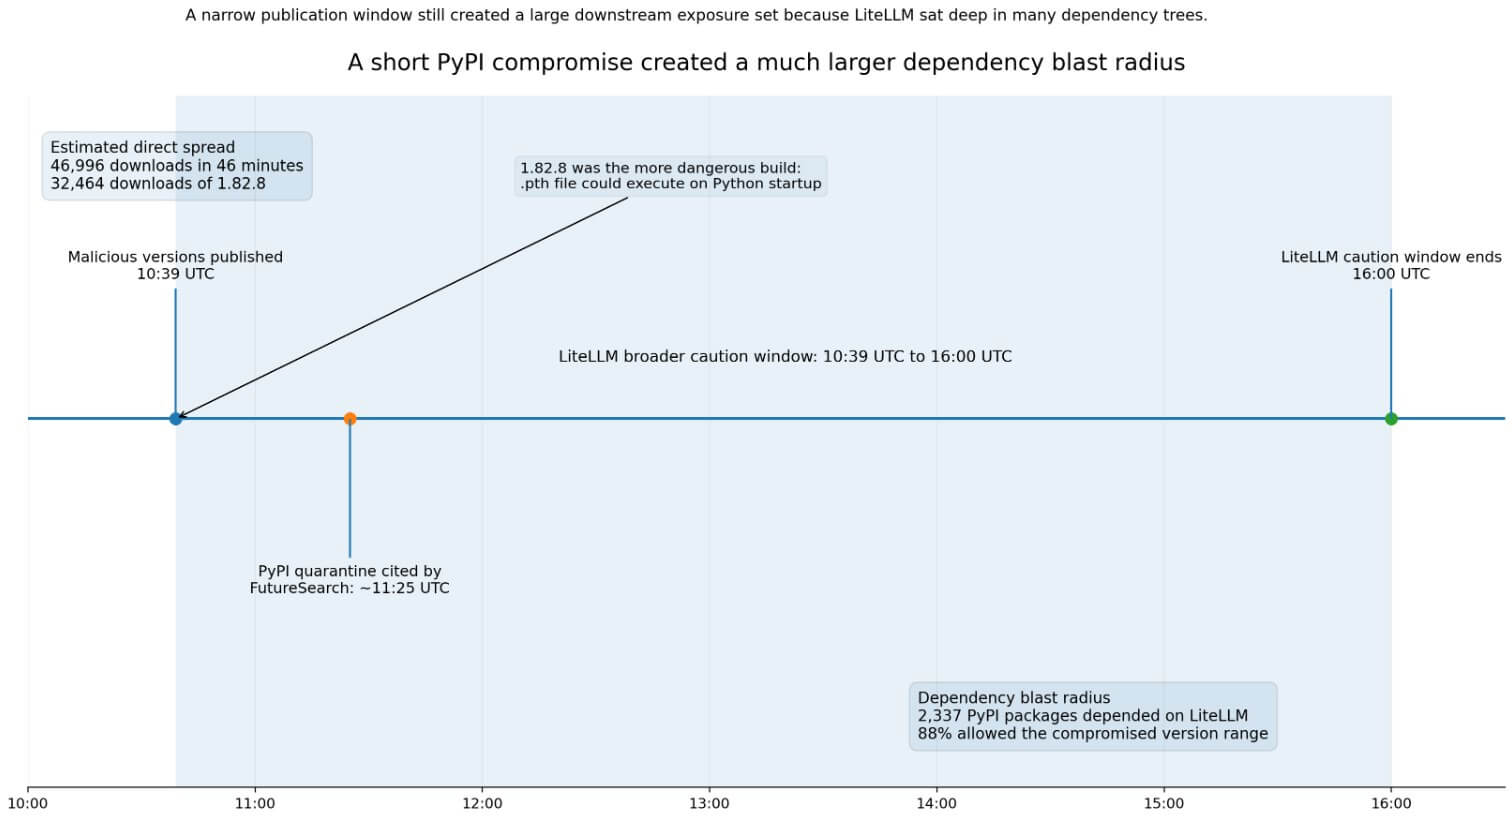
On Mar. 24, between 10:39 UTC and 16:00 UTC, an attacker who had gained entry to a maintainer account revealed two malicious variations of LiteLLM to PyPI: 1.82.7 and 1.82.8.
LiteLLM markets itself as a unified interface to greater than 100 massive language mannequin suppliers, a place that locations it inside credential-rich developer environments by design. PyPI Stats information 96,083,740 downloads within the final month alone.
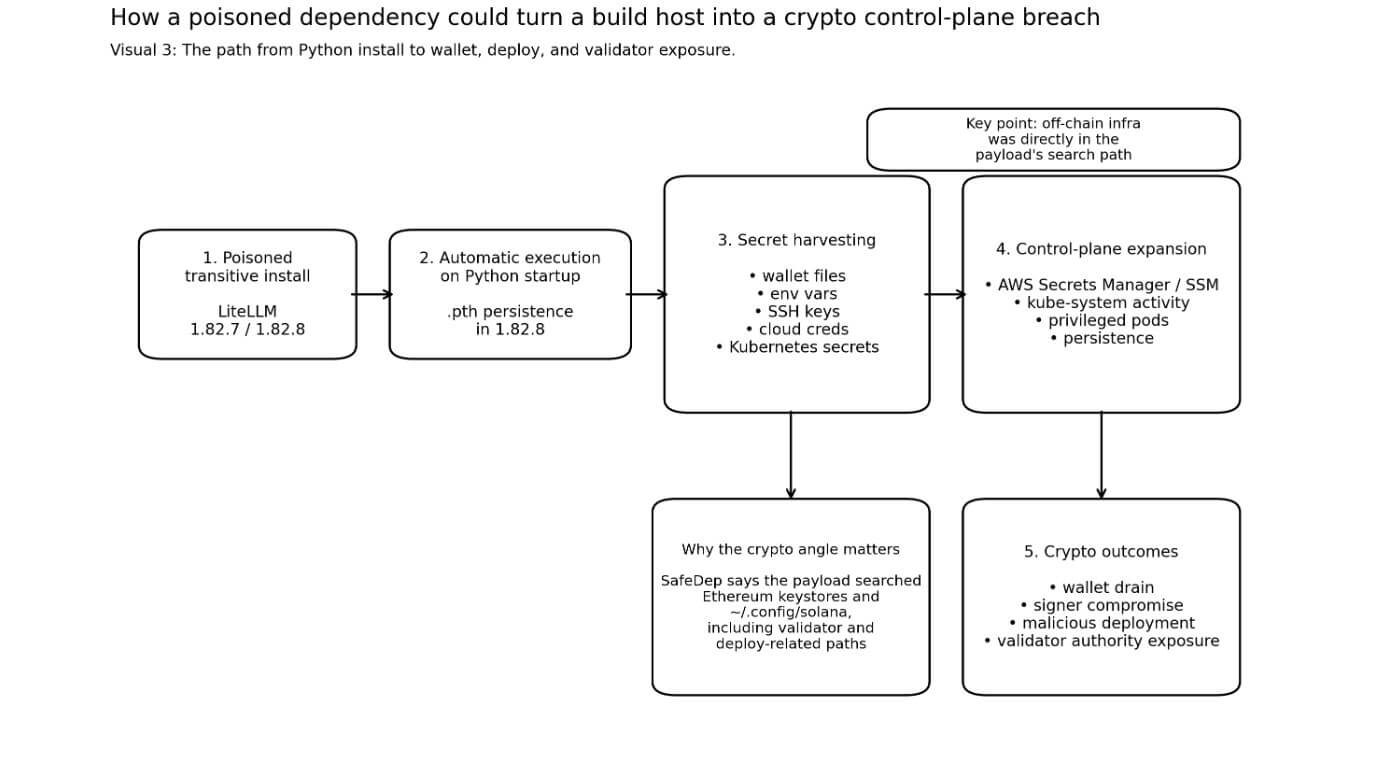
The 2 builds carried completely different ranges of danger. Model 1.82.7 required a direct import of litellm.proxy to activate its payload, whereas model 1.82.8 planted a .pth file (litellm_init.pth) within the Python set up.
Python’s personal documentation confirms that executable traces in .pth information run at each Python startup, so 1.82.8 executed with none import in any respect. Any machine that had it put in ran compromised code the second Python subsequent launched.
FutureSearch estimates 46,996 downloads in 46 minutes, with 1.82.8 accounting for 32,464 of them.
Moreover, it counted 2,337 PyPI packages that relied on LiteLLM, with 88% permitting the compromised model vary on the time of the assault.
LiteLLM’s personal incident web page warned that anybody whose dependency tree pulled in LiteLLM via an unpinned transitive constraint through the window ought to deal with their surroundings as doubtlessly uncovered.
The DSPy staff confirmed it had a LiteLLM constraint of “superior or equal to 1.64.0” and warned that contemporary installs through the window may have resolved to the poisoned builds.
Constructed to hunt crypto
SafeDep’s reverse engineering of the payload makes the crypto focusing on express.
The malware looked for Bitcoin pockets configuration information and pockets*.dat information, Ethereum keystore directories, and Solana configuration information underneath ~/.config/solana.
SafeDep says the collector gave Solana particular therapy, exhibiting focused searches for validator key pairs, vote account keys, and Anchor deploy directories.
Solana’s developer documentation units the default CLI keypair path at ~/.config/solana/id.json. Anza’s validator documentation describes three authority information central to validator operation, and states that theft of the approved withdrawer provides an attacker full management over validator operations and rewards.
Anza additionally warns that the withdrawal key ought to by no means sit on the validator machine itself.
SafeDep says the payload harvested SSH keys, surroundings variables, cloud credentials, and Kubernetes secrets and techniques throughout namespaces. When it discovered legitimate AWS credentials, it queried AWS Secrets and techniques Supervisor and the SSM Parameter Retailer for extra info.
It additionally created privileged node-setup-*pods in kube-system and put in persistence via sysmon.py and a systemd unit.
For crypto groups, the compounded danger runs in a specific direction. An infostealer that collects a pockets file alongside the passphrase, deploy secret, CI token, or cluster credential from the identical host can convert a credential incident right into a pockets drain, a malicious contract deployment, or a signer compromise.
The malware assembled precisely that mixture of artifacts.
| Focused artifact | Instance path / file | Why it issues | Potential consequence |
|---|---|---|---|
| Bitcoin pockets information | pockets*.dat, pockets config information |
Might expose pockets materials | Pockets theft danger |
| Ethereum keystores | ~/.ethereum/keystore |
Can expose signer materials if paired with different secrets and techniques | Signer compromise / deployment abuse |
| Solana CLI keypair | ~/.config/solana/id.json |
Default developer key path | Pockets or deploy authority publicity |
| Solana validator authority information | validator keypair, vote-account keys, approved withdrawer | Central to validator operations and rewards | Validator authority compromise |
| Anchor deploy directories | Anchor-related deployment information | Can expose deploy workflow secrets and techniques | Malicious contract deployment |
| SSH keys | ~/.ssh/* |
Opens entry to repos, servers, bastions | Lateral motion |
| Cloud credentials | AWS/GCP/Azure env or config | Expands entry past the native host | Secret-store entry / infra takeover |
| Kubernetes secrets and techniques | cluster-wide secret harvest | Opens management aircraft and workloads | Namespace compromise / lateral unfold |
This assault is a part of a wider marketing campaign, as LiteLLM’s incident note hyperlinks the compromise to the sooner Trivy incident, and Datadog and Snyk each describe LiteLLM as a later stage in a multi-day TeamPCP chain that moved via a number of developer ecosystems earlier than reaching PyPI.
The focusing on logic runs persistently throughout the marketing campaign: a secret-rich infrastructure tooling offers quicker entry to wallet-adjacent material.
Potential outcomes for this episode
The bull case rests on the pace of detection and the absence, to date, of publicly confirmed crypto theft.
PyPI quarantined each variations by roughly 11:25 UTC on Mar. 24. LiteLLM eliminated the malicious builds, rotated maintainer credentials, and engaged Mandiant. PyPI at present reveals 1.82.6 as the most recent seen launch.
If defenders rotated secrets and techniques, audited for litellm_init.pth, and handled uncovered hosts as burned earlier than adversaries may convert exfiltrated artifacts into lively exploitation, then the harm stays contained to credential publicity.
The incident additionally accelerates the adoption of practices already gaining floor. PyPI’s Trusted Publishing replaces long-lived handbook API tokens with short-lived OIDC-backed identification, roughly 45,000 initiatives had adopted it by November 2025.
LiteLLM’s incident concerned the abuse of launch credentials, making it a lot tougher to dismiss the case for switching.
For crypto groups, the incident creates urgency for tighter function separation: cold validator withdrawers saved totally offline, remoted deployment signers, short-lived cloud credentials, and locked dependency graphs.
The DSPy staff’s fast pinning and LiteLLM’s personal post-incident steerage each level towards airtight builds because the remediation normal.
The bear case activates lag. SafeDep documented a payload that exfiltrated secrets and techniques, unfold inside Kubernetes clusters, and put in persistence earlier than detection.
An operator who put in a poisoned dependency inside a construct runner or cluster-connected surroundings on Mar. 24 could not uncover the complete scope of that publicity for weeks. Exfiltrated API keys, deploy credentials, and pockets information don’t expire on detection. Adversaries can maintain them and act later.
Sonatype places malicious availability at “at the very least two hours”; LiteLLM’s personal steerage covers installs via 16:00 UTC; and FutureSearch’s quarantine timestamp is 11:25 UTC.
Groups can’t rely solely on timestamp filtering to find out their publicity, as these figures don’t yield a transparent all-clear.
Essentially the most harmful state of affairs on this class facilities on shared operator environments. A crypto trade, validator operator, bridge staff, or RPC supplier that put in a poisoned transitive dependency inside a construct runner would have uncovered a whole management aircraft.
Kubernetes secret dumps throughout namespaces and privileged pod creation within the kube-system namespace are control-plane entry instruments designed for lateral motion.
If that lateral motion reached an surroundings the place scorching or semi-hot validator materials was current on reachable machines, the results may vary from particular person credential theft to compromise of validator authority.
PyPI’s quarantine and LiteLLM’s incident response closed the lively distribution window.
Groups that put in or upgraded LiteLLM on Mar. 24, or that ran builds with unpinned transitive dependencies resolving to 1.82.7 or 1.82.8, ought to deal with their environments as totally compromised.
Some actions embody rotating all secrets and techniques accessible from uncovered machines, auditing for litellm_init.pth, revoking and reissuing cloud credentials, and verifying that no validator authority materials was accessible from these hosts.
The LiteLLM incident paperwork a path of an attacker who knew precisely which off-chain information to search for, had a supply mechanism with tens of hundreds of thousands of month-to-month downloads, and constructed persistence earlier than anybody pulled the builds from distribution.
The off-chain equipment that strikes and safeguards crypto sat instantly within the payload’s search path.
You might also like


More from Web3

Bitcoin’s Sharpest Rally in Two Years Ran Almost Entirely on Short Liquidations
In short Over 5 days in August, Bitcoin rose 24.6% whereas coin-denominated open curiosity fell 12.6%, which means the rally …

Grayscale Is Making Its Red-Hot Zcash ETF More Affordable
In short Grayscale's Zcash ETF (ZCSH) will do a 3-for-1 ahead share break up, with new shares paid out Sept. …

Solana’s Heartbeat Quickens: Block Times Fall 17% in Latest Speed Upgrade
In short Solana's goal slot time—the window a validator will get to provide a block—dropped from 300 milliseconds to 250 …


